
Websites are becoming more aggressive about detecting automated traffic, using browser, network, and behavioural signals to distinguish bots from ordinary users. Cloudflare estimates that bots account for around 30% of global web traffic, while its 2025 analysis found that 546 of 3,816 domains examined had robots.txt rules specifically targeting AI crawlers.
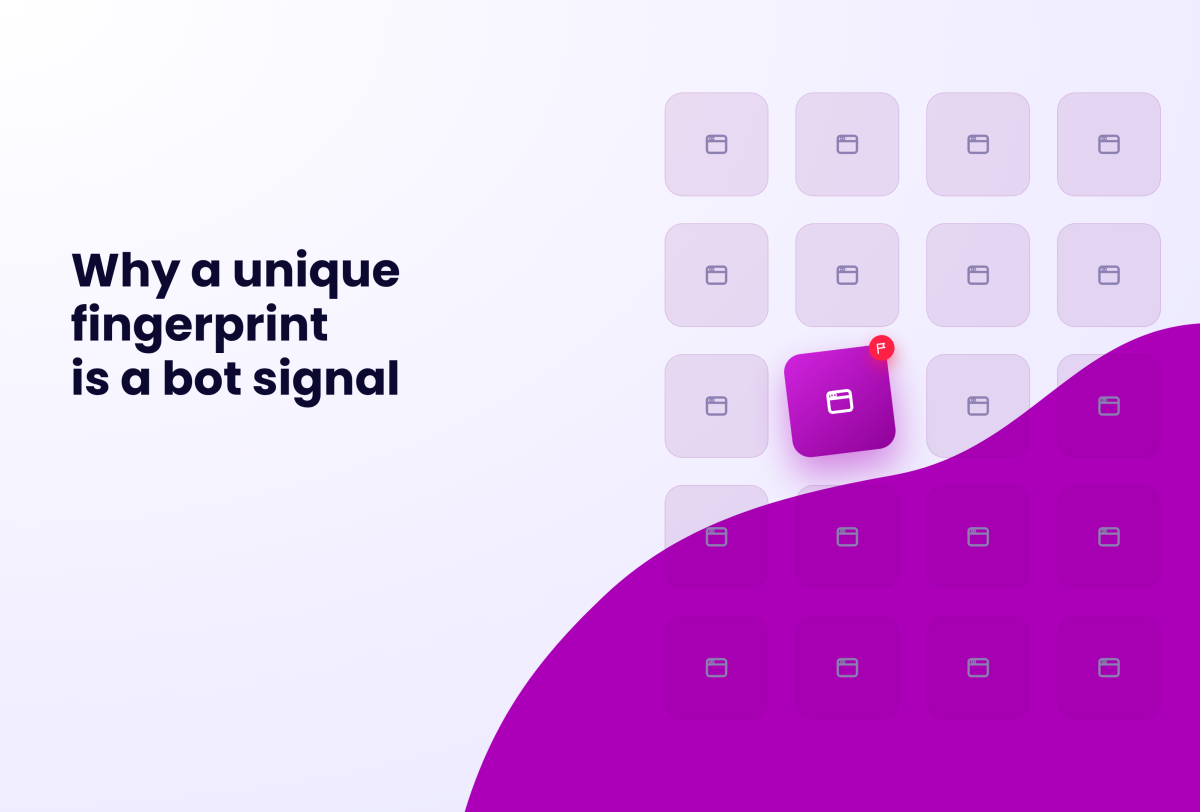
Browser fingerprinting is one of the signals websites can use to identify unusual or automated traffic. For users of anti-detect browsers, this creates an important consideration: modifying your browser fingerprint does not automatically make a profile look more legitimate. If the changes produce a rare, contradictory, or unstable combination of characteristics, the modified fingerprint can become another signal that a detection system uses to flag the profile.
In this article, we will look at what makes up a browser fingerprint, how an unusual fingerprint can become a bot signal, and the basic practices that can help you manage fingerprints more consistently.
The Anatomy of a Browser Fingerprint
To understand why a unique fingerprint serves as a red flag, we must first understand what constitutes a "fingerprint". A browser fingerprint is a collection of characteristics that can be observed by a website when a browser loads a page. These can include:
- User-agent information: Details about the browser, operating system and rendering engine.
- System and browser settings: Timezone, language, screen configuration and other available properties.
- WebGL properties: Information about graphics capabilities, including the GPU vendor and renderer.
- Canvas and audio characteristics: Results produced when the browser processes specific graphics or audio operations.
Individually, many of these attributes are common. Millions of people may use the same browser or operating system. The identifying value comes from the combination.
For example, knowing that someone uses Chrome on Windows tells a website relatively little. There are enormous numbers of Chrome-on-Windows users.
Add an unusual screen configuration, a rare combination of fonts, and a particular graphics configuration, however, and the resulting combination becomes more distinctive.
Websites can also use techniques such as canvas and AudioContext fingerprinting to collect additional information. Canvas fingerprinting examines how a browser renders a particular image, while AudioContext fingerprinting can examine how the browser and underlying hardware process audio.
When these data points are combined, they create a "digital signature" that is nearly impossible to replicate perfectly across different devices, yet stable enough to track you across different websites.
How Can a Unique Fingerprint Become a Bot Signal?
Bot detection systems generally do not rely on one piece of information to determine whether traffic is automated. Instead, they can evaluate multiple signals and assign different levels of significance to them. A fingerprint that is unusually rare may become more important when it appears alongside other suspicious characteristics.
For example, consider a browsing environment with an unusual fingerprint that also:
- appears across many new accounts;
- changes characteristics between sessions;
- contains inconsistent browser settings;
- produces unusual interaction patterns;
- connects from a network associated with other automated traffic.
None of these signals necessarily proves automation by itself. Together, however, they can give a detection system more reason to investigate the traffic.
What Makes a Fingerprint Look Unusual?
There is no universal list of characteristics that make a fingerprint "bot-like." What is unusual depends on the website, its user population, and the detection system being used.
However, several patterns can make a fingerprint more distinctive.
Rare combinations
A single uncommon attribute may not matter much. Several uncommon attributes appearing together can make a fingerprint substantially more distinctive. A browser using an uncommon operating system may be perfectly normal. The same browser combined with an unusual screen configuration, graphics setup, and other rare characteristics may be much less common.
This is why changing several fingerprint attributes at random can have the opposite effect from what the user intended. Instead of blending into a larger group of similar browsers, the resulting combination may become more unusual.
Internal inconsistencies
Different parts of the browser environment can sometimes provide conflicting information. For example, the reported browser, operating system, hardware characteristics, and other properties may not form a combination normally associated with one another. The problem is not that one attribute is unusual. It is that the attributes do not appear to belong to the same environment.
Excessive instability
Frequent changes to characteristics that should normally remain stable can make a browsing environment unusual. If a profile repeatedly presents different browser, operating system, or hardware characteristics between sessions, that change can become another signal for a detection system.
Fingerprint reuse
The opposite problem can also occur. If many supposedly separate users repeatedly present the same unusual browser fingerprint, a system may have a reason to connect those sessions.
This matters when multiple browser profiles are managed from the same machine. Creating several profiles is not enough if those profiles repeatedly expose the same identifying characteristics.
Practical Steps for Better Fingerprint Hygiene
If you use an anti-detect browser like Incogniton that allows you to modify a whole set of parameters that make up your browser fingerprint, it is important to maintain certain laid-out best practices so you don't shoot yourself in the foot. As we have discussed in other Incogniton articles, a realistic browser profile should present a coherent set of characteristics rather than a collection of randomly modified values.
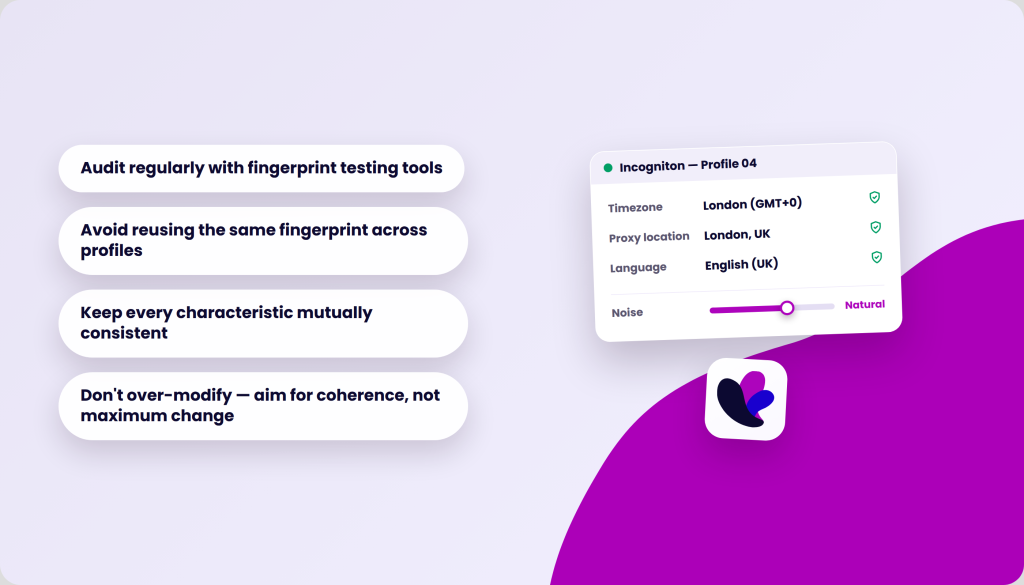
Here are some practical rules to follow when managing multiple browser fingerprints across different profiles:
Audit regularly
Use browser fingerprint testing tools like Pixelscan to check for leaks in your setup. If you see a mismatch between your reported OS and your WebGL renderer, fix it in your Incogniton profile settings.
Avoid profile reuse
If separate browser profiles are intended for separate workflows, keep their browser identities and session data separated. Reusing the same unusual fingerprint across multiple profiles can undermine that separation.
Maintain consistency
The characteristics exposed by a profile should make sense together. Browser settings, operating system information, graphics characteristics, and other fingerprint attributes should not contradict one another.
Network information is another part of the picture. A profile that consistently presents one environment while repeatedly connecting through networks that suggest a very different location or setup may create additional inconsistencies.
If you set a profile to represent a user in London, ensure your proxy is in London, your language is set to English (UK), and your system time is configured accordingly.
Do not over-modify the fingerprint
A common mistake among beginners is trying to block all fingerprinting scripts. Changing as many signals as possible is not necessarily better because excessive modification can create an unusual combination of characteristics of its own.
Instead, the goal is coherence. Your timezone must match your IP location; your screen resolution must match your device type; and your GPU vendor must match your operating system. When these elements tell a consistent story, detection systems are far less likely to label you as a bot.
If you use Incogniton, use the "Noise" settings in Incogniton to introduce natural-looking variations. It help you control how these characteristics are presented across profiles.
Conclusion
A unique browser fingerprint is not automatically a bot signal. What matters is how rare the combination is, whether its characteristics are internally consistent, how stable it remains between sessions, and whether the same fingerprint appears across multiple profiles or accounts.
For anti-detect browser users, fingerprint management is therefore less about making a profile as different as possible and more about maintaining a coherent browser environment. A fingerprint that makes sense as a whole is less likely to raise questions than one built from unrelated or constantly changing attributes.