
A social media manager brings on a freelancer for the week. Before the freelancer can schedule a single post, there are logins to hand over, verification codes to forward, and a security alert to clear because the login came from a new city. Multiply that by fifteen client accounts and three more teammates, and access management becomes a job of its own.
Working as a team on online platforms has always had this weak spot. Most platforms are built around one person and one login, so teams get around it by sharing passwords. That workaround creates problems that grow with every account and every person you add.
In an earlier post, we covered how to use Incogniton for team management and collaboration. Now we're looking at the bigger operational question: how do you scale team access without losing control?
Why Sharing Passwords Doesn’t Scale
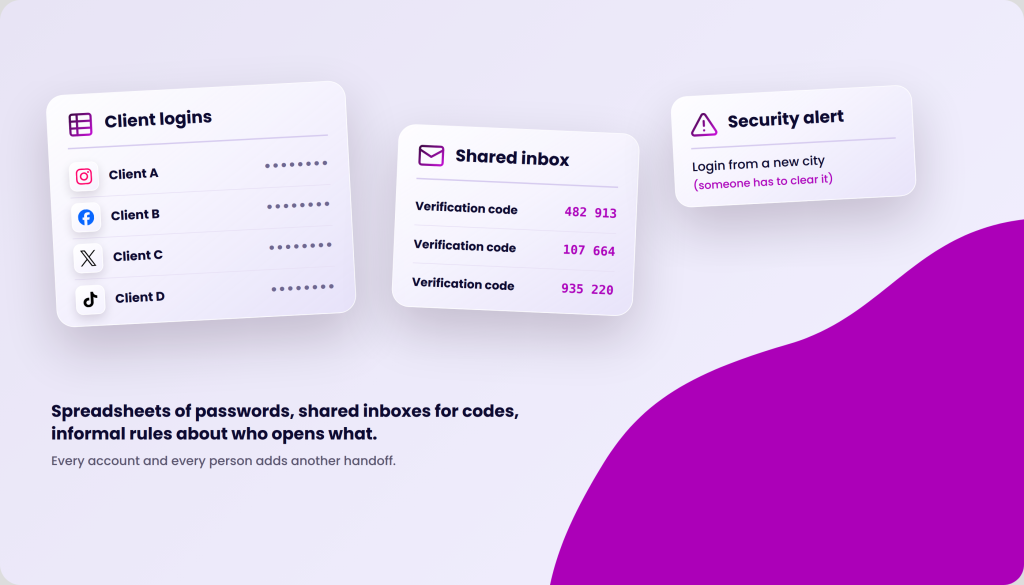
When you are managing a workflow that involves using online platforms across a team, password sharing may feel convenient at first, but it carries three costs.
First, it weakens security. Once a password is shared, you lose visibility over who has access, whether it was copied, and where it might end up. If a contractor leaves or a role changes, you may not know whether they still have the login.
Second, it hurts accountability. When several people use the same credentials, audit trails become messy. If something goes wrong in an ad account or storefront, it’s harder to determine who made the change.
Third, it disrupts workflows. Teams end up waiting on one another, getting locked out by suspicious login alerts, or dealing with platforms that flag logins from different IPs or devices. For agencies and operators managing multiple client or brand accounts, that friction adds up fast.
The problem multiplies when a team runs many accounts. Social media management companies handle dozens of client accounts across Instagram, Facebook, X, and TikTok, with different people responsible for different clients. Affiliate marketers and media buyers run several ad accounts at once, often with more than one person working inside each.
Teams end up with spreadsheets of passwords, shared inboxes for verification codes, and informal rules about who opens what. Mistakes are easy in this setup. Someone opens the wrong account from the wrong browser, and accounts that were supposed to stay separate suddenly share a footprint. Platforms look at signals like IP address and browser fingerprint when deciding whether accounts are related, so one careless login can link accounts, trigger a review, or get an account restricted.
A better model is role-based access with controlled browser sessions and profile sharing, where people get the access they need without ever seeing the underlying password. And this is what Incogniton anti-detect browser offers.
How Incogniton Supports Permission-Based and Passwordless Team Collaboration
If you don't know Incogniton already, it is an anti-detect browser that allows you to browse the internet on your own terms, truly anonymously and privately. Each browser profile gets its own fingerprint, cookies, and proxy, so the accounts you run stay separate from one another.
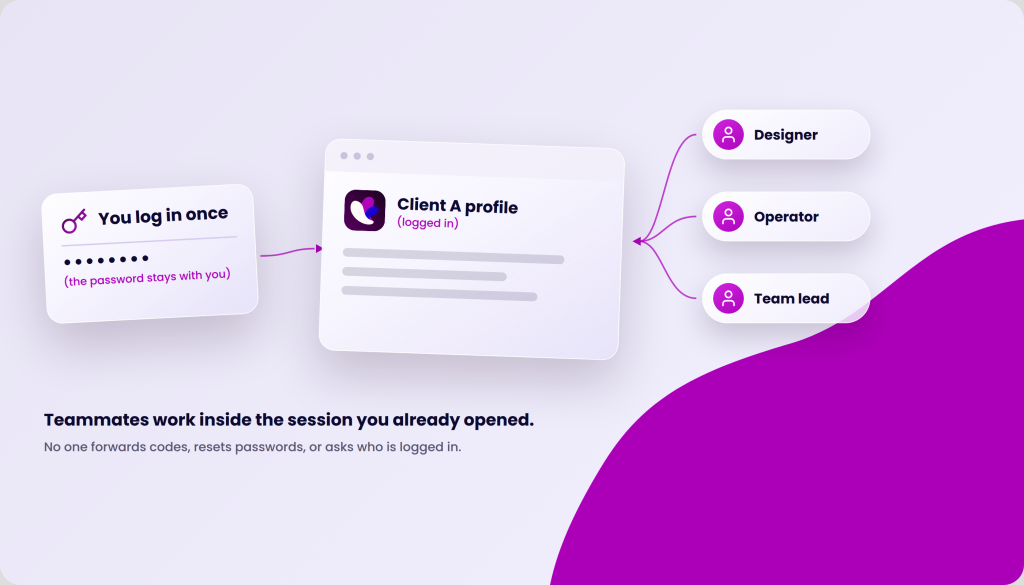
One of its key features is team collaboration. Instead of handing over your passwords and credentials, you give teammates access to the browsing session you are already working in. The login happens once, and the rest of the team works inside the session. No one has to forward codes, reset passwords, or ask who is currently logged in.
If you've shared a Google Doc, you already understand the model. You decide who gets in and what they can do once they're there, and you can change or take that back whenever you need to. Incogniton's team feature applies the same idea to browsing sessions and profile groups.
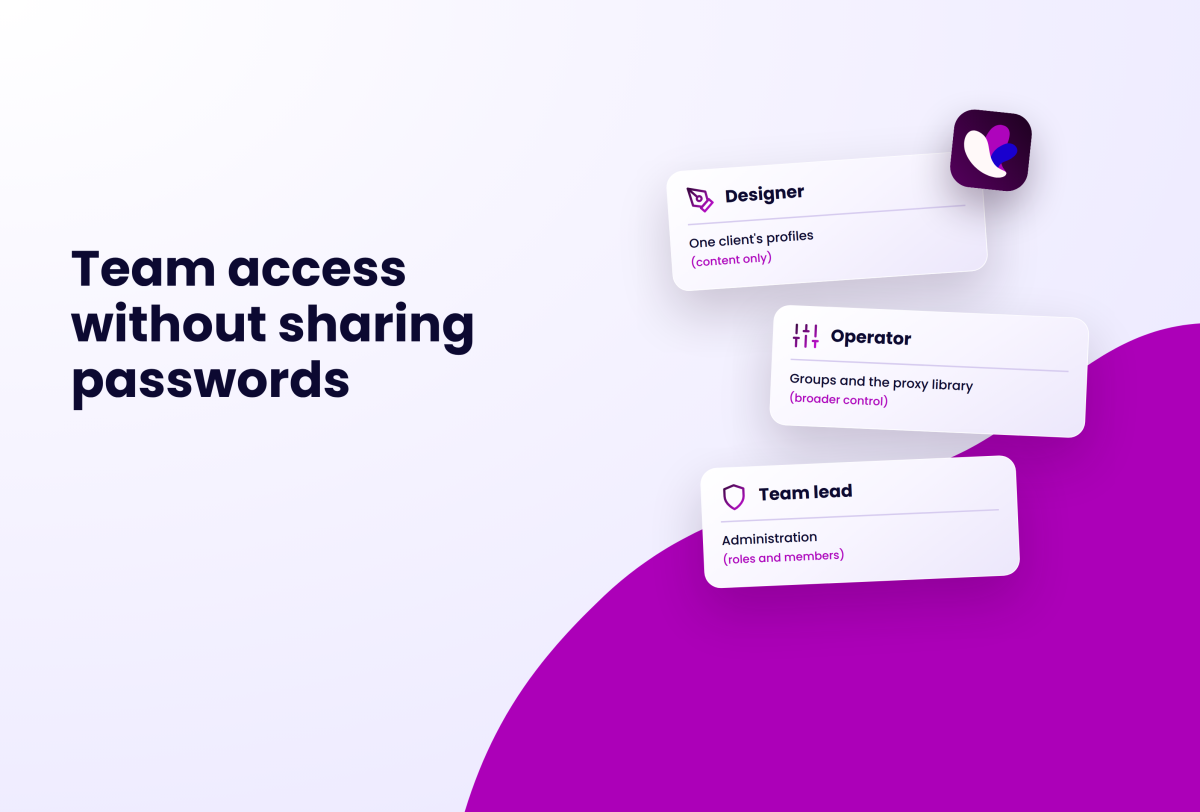
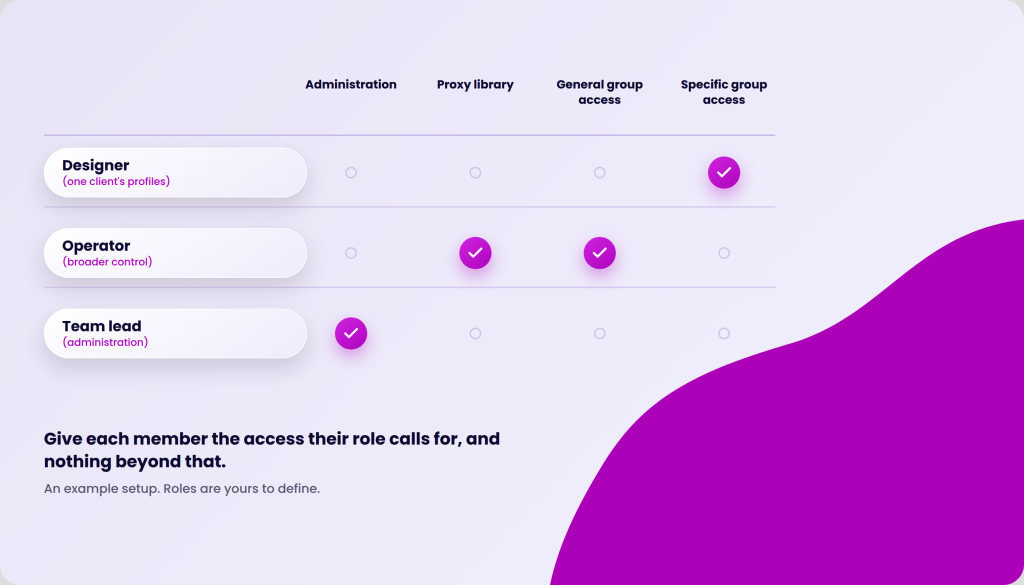
Admins create roles and choose the permissions attached to each member. These permissions can cover administration, the proxy library, general group access, and specific group access. In practice, a designer might only get access to one client's content profiles, an operator might get broader control that includes proxies, and a team lead might handle administration.
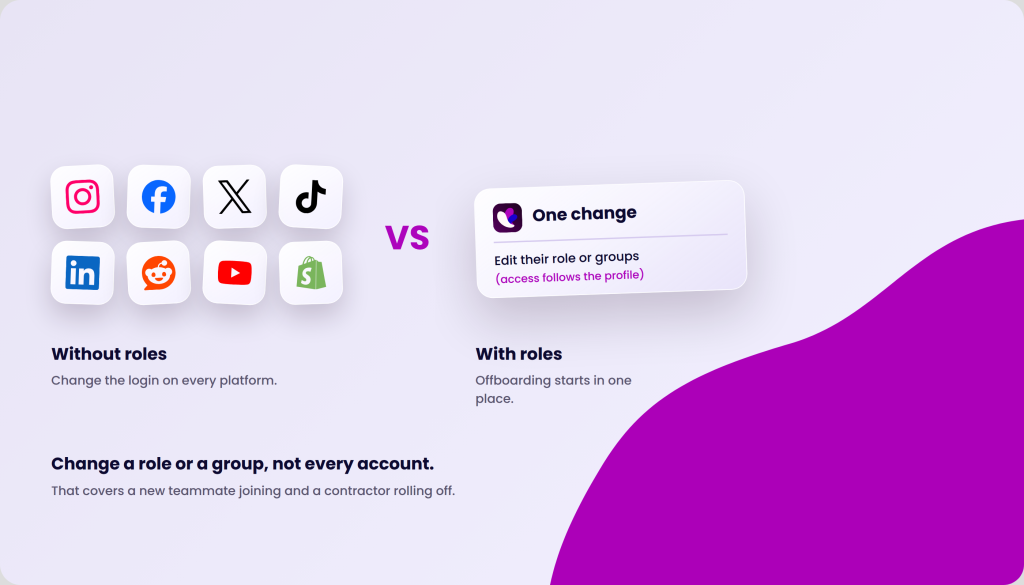
Because members can be given entire groups of profiles, you can organize accounts by client or project and share a group instead of granting access to one profile at a time. When a new teammate joins, or a contractor rolls off, you change their role or their groups instead of touching every account.
There are limits worth knowing. The team feature is available on the Professional plan and above. And sharing access doesn't change how a platform treats behavior: a shared profile that suddenly acts out of character can still get flagged. Permissions control who can do what. They don't replace good habits.
READ MORE: Common Mistakes When Running Multiple Accounts in an Antidetect Browser
How to Set up Incogntion for Passwordless Team Collaboration
Here is a simple guide to get started with passwordless team collaboration with Incogniton.
Check your plan
Team features on Incogniton are available from the Professional plan upward. So if you are on that plan, you will have to upgrade. If you are on that plan or higher, proceed to the next step.
Create roles first
Open Incogniton and navigate to the Roles tab on the dashboard. Click New role, name it, choose the permissions, and create it.
Tip: Keep administration permissions limited to team leads or account owners, and build separate roles for the people who only need to work inside specific accounts.
Organize profiles into groups
Group accounts by client, brand, or project. It is much easier to share and revoke a group than to manage dozens of individual profiles.
Invite your team members
Go to the Team tab and click Invite member. Fill in their details, choose whether they set their own password or you set it for them, assign a role, and send the invite. You can change the role later.
Share the right groups
Give each member the profile groups their role calls for, and nothing beyond that.
Review access regularly
Team admins can use the Activity tab to see login history, failed logins, browser profile sessions, and total active time per member, and export the results as CSV or Excel. Use it to spot inactive users, adjust roles when responsibilities change, and close gaps left by freelancers.
Conclusion
Sharing passwords was never a real system for team access. It was a workaround that gets more expensive with every account and person you add. For agencies, social media management companies, and affiliate teams, the cost shows up as slow handoffs, login alerts, muddy accountability, and the risk of one wrong login linking accounts that should stay apart.
Passwordless team collaboration is only one part of why Incogniton anti-detect browser is perfectly suited for multi-accounting. It also has other features that cut the daily grind: a built-in proxy marketplace, the Cookie Collector for building browsing history, and API support for Selenium, Puppeteer, and Playwright to automate repetitive tasks. Together, they take manual work out of running many accounts.