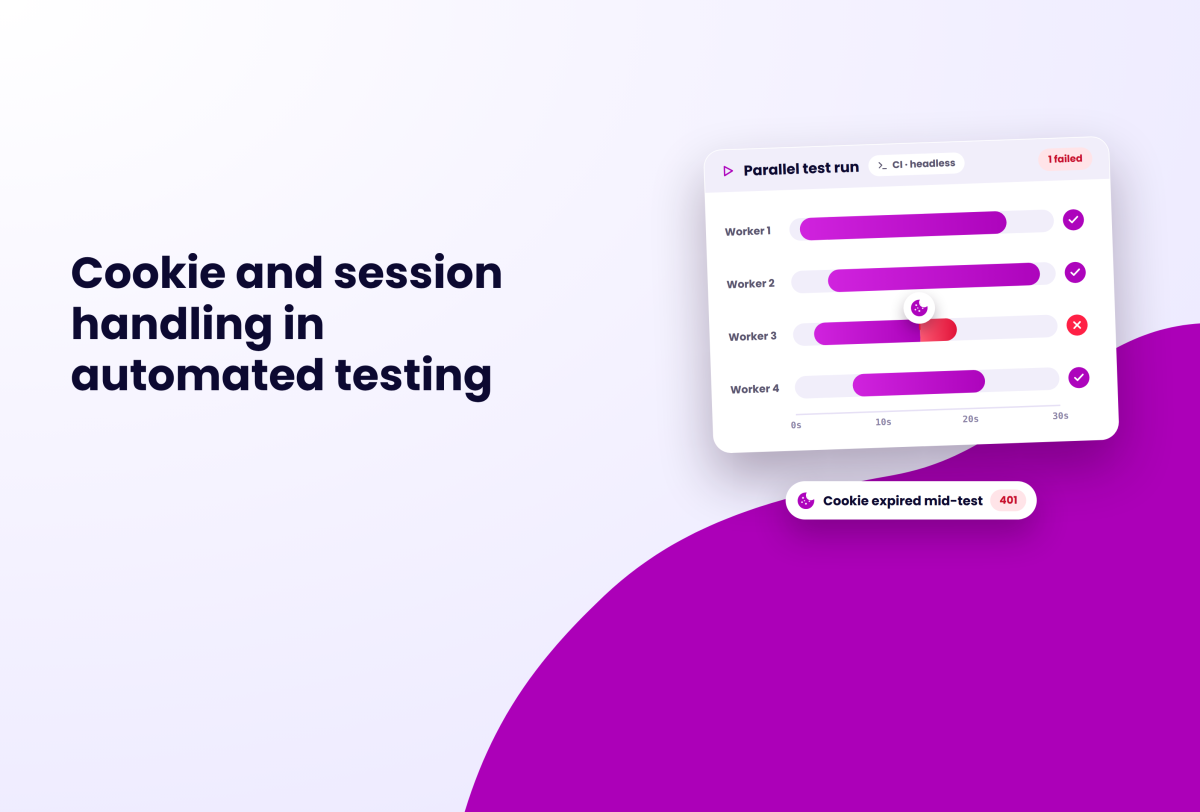

Cookie and session handling is one of the most common reasons automated tests fail. Authentication and session-state issues can turn stable-looking test suites into flaky failures, delayed deployments, and false positives.
As development teams speed up release cycles with continuous integration and browser automation, the web is also changing. Third-party cookies are being phased out, SameSite defaults are stricter, and websites increasingly combine cookies with browser fingerprinting and other security checks. A test that works locally can fail in a headless browser or a parallel test run because a cookie expired, was never saved, or no longer matches the browser environment.
This article explains why cookie and session failures happen, how to fix them, and how to prevent them from happening in the first place.
How cookies and sessions work together
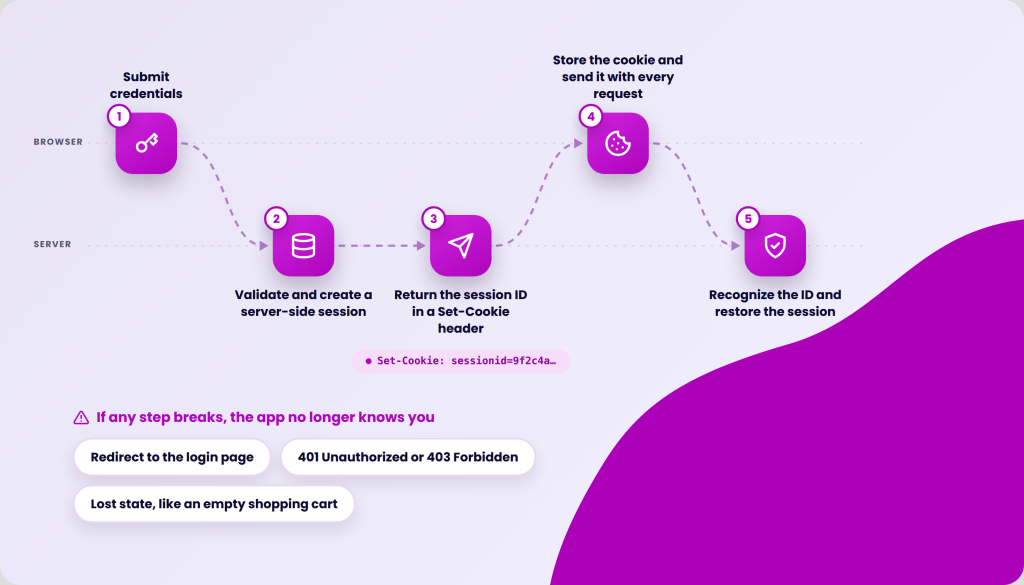
Cookies and sessions are closely related, but they serve different purposes. Cookies are small pieces of data stored in the browser, while sessions are usually stored on the server and keep track of a user's authenticated state.
They work together to create a continuous browsing experience. Instead of storing an entire session in the browser, the server typically stores the session data and sends the browser a session ID inside a cookie. Every time the browser makes another request, it sends that cookie back, allowing the server to recognize the user and restore their session.
A typical login flow looks like this:
- The user submits their credentials.
- The server validates them and creates a server-side session.
- The server returns a session identifier in a Set-Cookie header.
- The browser stores the cookie and includes it with future requests.
- The server recognizes the session ID and restores the user's authenticated state.
If this process breaks at any point, the application can no longer recognize the user. In automated testing, that often results in a redirect to the login page, a 401 Unauthorized or 403 Forbidden response, or lost application state, such as an empty shopping cart.
Why Cookies and Sessions Matter in Automated Testing
Every browser test depends on state. When a user logs in, adds items to a cart, changes account settings, or moves between pages, the browser has to remember who that user is. Cookies and sessions provide that memory.
Without them, every page request looks like it comes from a brand-new visitor. A test that is supposed to verify a checkout flow, user dashboard, or admin panel cannot continue if the application no longer recognizes the logged-in user.
This is why cookie and session management affects almost every type of browser automation, including:
- Login and authentication testing
- Checkout and payment flows
- Multi-page form testing
- Account management features
- Role-based access testing
- End-to-end regression tests
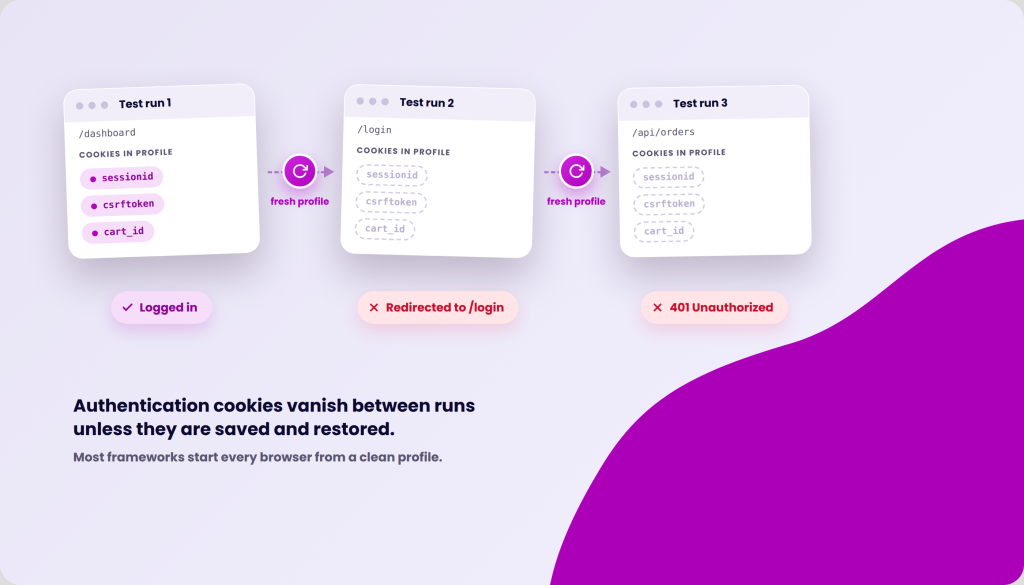
In manual browsing, the browser handles cookies automatically, so users rarely think about them. Automated tests work differently. Most testing frameworks intentionally start with a clean browser profile, which means there are no saved cookies, cached credentials, or browsing history.
READ MORE: How to Use Incogniton with RTILA to Automate Your Workflow
That creates several challenges. A new browser session starts as if it has never visited the website, authentication cookies disappear between test runs unless they are saved and restored, and browser state can behave differently across headless browsers, parallel test runs, and continuous integration (CI) environments.
These differences are what make cookie and session handling one of the most common causes of flaky browser tests. The next section looks at the specific reasons these failures happen and how to fix them.
Common Reasons Why Automation Scripts Break
When authentication suddenly stops working, the root cause is often one of these issues.
1. Cookies Are Not Preserved Between Test Runs
Most WebDriver sessions start with a fresh browser profile. Every new browser instance begins without cookies, local storage, or cached credentials. If your test expects an existing login session, it will fail because the authentication cookie from the previous run no longer exists.
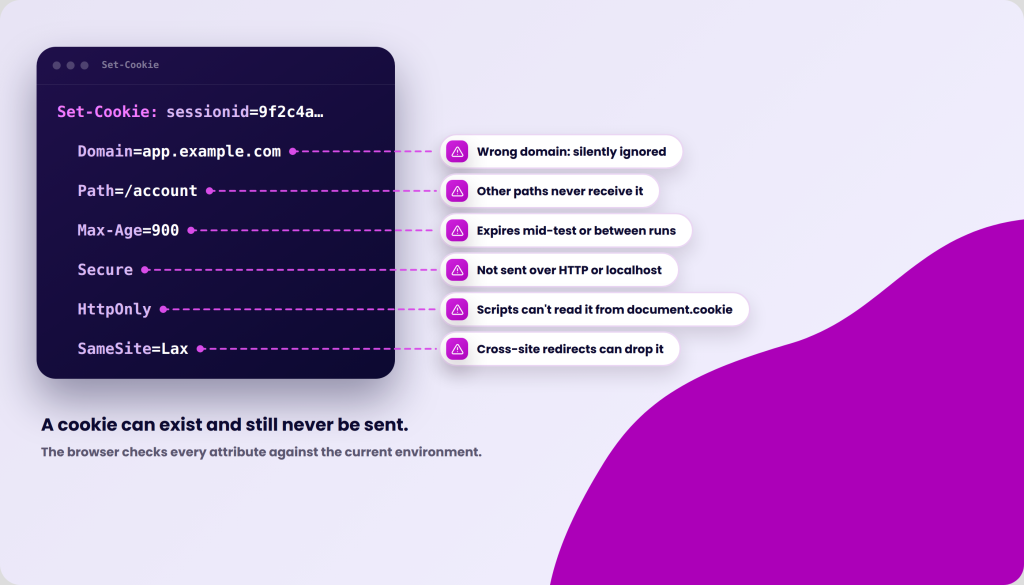
A common reason is that the browser accepts or rejects cookies based on their attributes. A cookie may exist, but the browser may refuse to send it if its settings don't match the current environment.
Cookie Attributes That Frequently Cause Problems
| Attribute | What It Does | Common Automation Issue |
| Domain | Defines which hosts may receive the cookie | Setting a cookie for the wrong domain causes it to be silently ignored |
| Path | Limits the cookie to a specific URL path | Tests hitting a different path may not receive the expected cookie |
| Expires/Max-Age | Controls cookie lifetime | Short-lived cookies expire mid-test or between test runs |
| Secure | Restricts the cookie to HTTPS connections | Cookies are not sent over HTTP, breaking tests that use localhost or HTTP |
| HttpOnly | Prevents JavaScript access to the cookie | Selenium or Puppeteer scripts cannot read the cookie via document.cookie |
| SameSite | Controls cross-site request behavior (Strict, Lax, None) | Cross-origin redirects, or iframes may lose session cookies |
2. Browser Fingerprinting Triggers Security Checks
Many websites use browser fingerprinting alongside cookies to detect unusual activity. If an automated browser presents an inconsistent or obviously automated fingerprint, the website may invalidate the session, reject authentication, or trigger a CAPTCHA.
This is why some automation workflows use isolated browser profiles. Tools such as Incogniton anti-detect browsers help keep browser fingerprints and stored cookies consistent across sessions.
3. Race Conditions During Page Loading
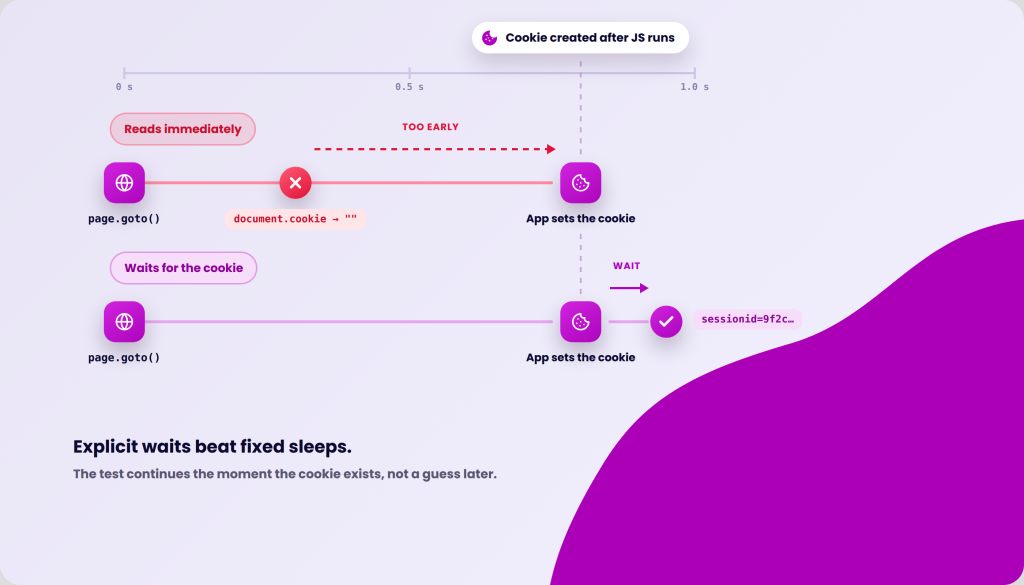
Modern frameworks such as React and Angular often create or update cookies after JavaScript finishes running. If a script reads or injects cookies before the page completes that process, the cookie may be missing or outdated, leading to intermittent failures that are difficult to reproduce.
Best Practices for Robust Cookie Management
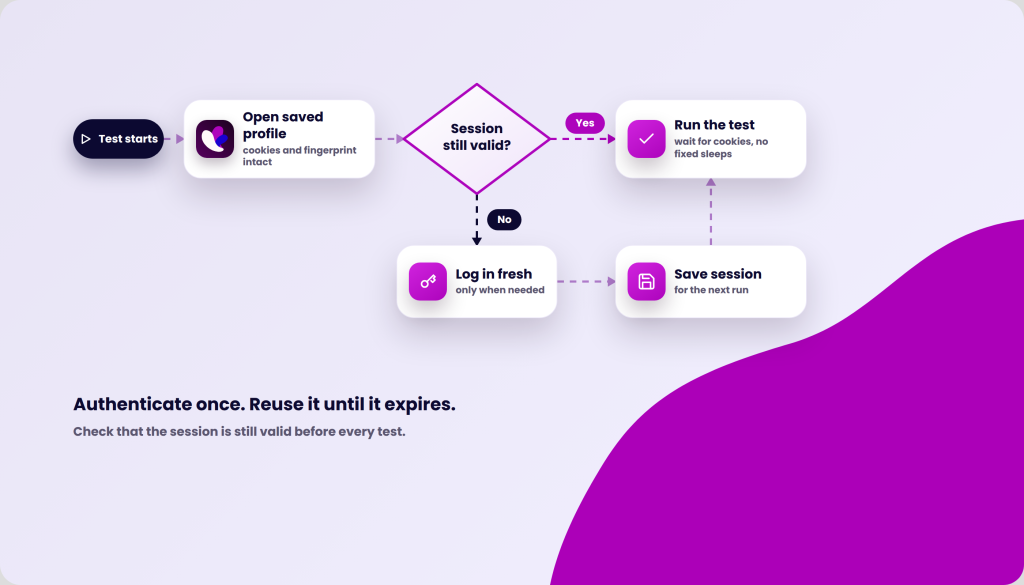
Reliable browser automation depends on managing browser state intentionally rather than assuming it will persist.
Reuse Sessions When Appropriate
Instead of logging in before every test, authenticate once, save the session cookies, and load them into later browser sessions when the application allows it.
This reduces execution time and avoids unnecessary authentication requests.
Keep Browser Profiles Isolated
Separate browser profiles prevent cookies, local storage, and other browser data from leaking between different test users or environments. Isolated profiles help maintain consistent browser identities across automation sessions.
Handle Cookie Expiration Gracefully
Sessions eventually expire. Instead of allowing a test to fail immediately, check whether the session is still valid and perform a fresh login only when necessary.
This approach makes long-running test suites more resilient.
Wait for Cookies to Be Created
Avoid reading or injecting cookies immediately after navigation. Wait until the application has finished creating the session before interacting with browser storage.
Explicit waits are generally more reliable than fixed sleep timers.
Conclusion
Cookie and session handling is a major source of instability in automated testing, but most failures have predictable causes. Fresh browser profiles, expired sessions, fingerprint mismatches, and timing issues can all break authentication even when the test logic is correct.
Managing browser state deliberately helps create more reliable test suites. Whether you use Selenium, Playwright, Puppeteer, or another automation framework, treating cookies and sessions as part of your test infrastructure is essential for consistent results.